




How long can digital certificates be valid? Go to How long can digital certificates be valid?
Learn about how the validity periods for digital certificates are...
Sectigo code signing certificates allow software publishers to digitally sign their code, including applications, executables, scripts, and programs, to confirm that the software has not been altered after release.
Without a digital signature verified by a trusted Certificate Authority (CA), major operating systems like Microsoft Windows will show end users a warning message before installation. This reduces downloads and adoption and leaves unsigned or weakly signed code vulnerable to tampering and supply-chain attacks.
Sectigo Code Signing certificates build user trust, protect against unauthorized modification, and support faster releases with streamlined issuance and reduced operational friction.
FIPS-compliant device delivery
Highest level of security
Bring your own hardware
Code signing shouldn't block releases or scare away users. Sectigo's verified certificates boost install rates, eliminate signing delays, and protect every build from unauthorized tampering.
OS security warnings + lost installs
Slow releases and DevOps friction
Risk of tampered code and supply chain attacks
Starting February 23, 2026, the CA/B Forum has changed the maximum certificate lifecycle for Code Signing certificates. Industry regulations require all Certificate Authorities to issue certificates no longer than 459 days (approximately 15 months). Certificate Authorities must ensure that the subscribers private key is generated stored and used in suitable FIPS-compliant hardware.
Requirements for private keys used with EV code signing certificates have been stronger than OV code signing certificates which are more relaxed.
The new rules are intended to reduce the potential misuse of code signing certificates and to further protect those certificates from getting into the wrong hands by making key protection requirements for OV code signing certificates the same as EV code signing certificates.
As of February 23, 2026, you will no longer be able to issue a single multi-year Code Signing certificate on a single FIPS-compliant device. Instead, if you purchase a multi-year Code Signing product from Sectigo you will receive a new compliant hardware device with a new certificate each year.
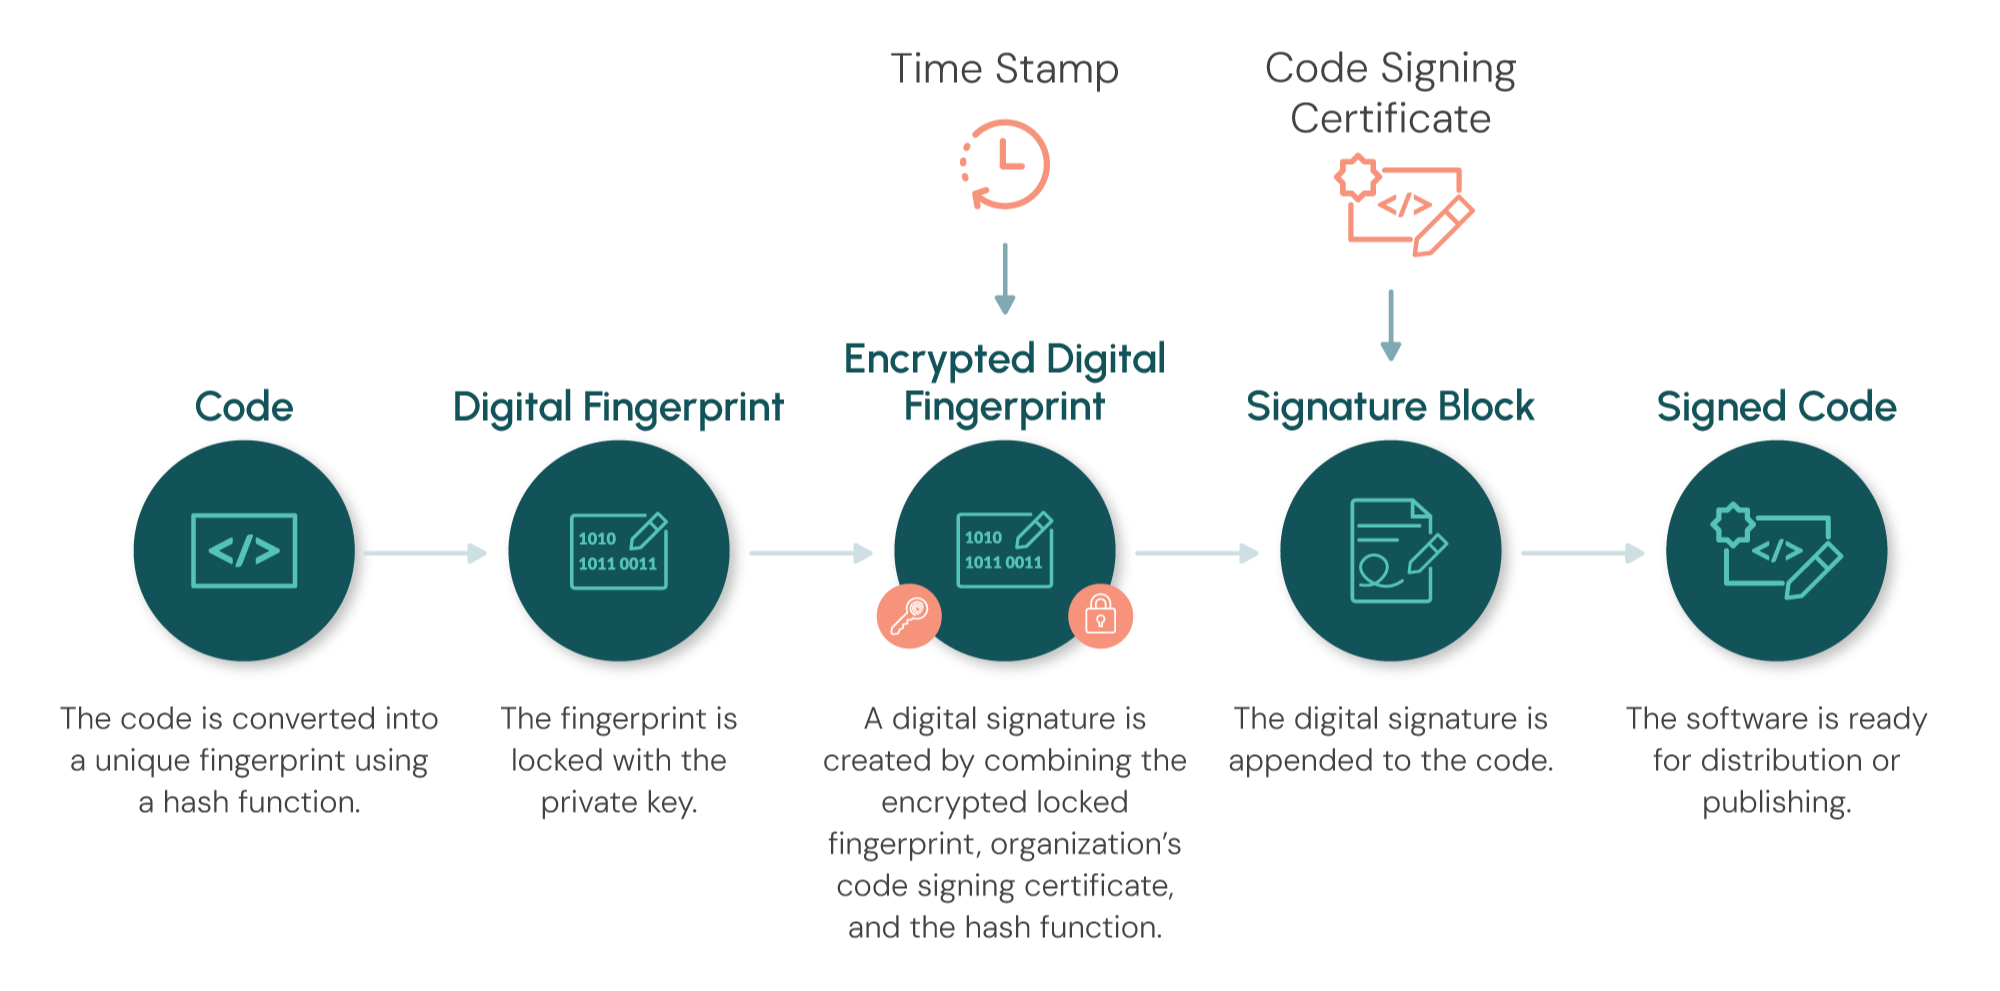
The code signing process works by using public key cryptography and cryptographic hashing to create a digital signature that binds a software package to a verified publisher identity. When code is signed, a unique fingerprint of the software is created, encrypted with the publisher’s private key, and attached to the code along with the code signing certificate so it can be verified before distribution.
When an end user downloads or installs the software, the operating system verifies the signature using the corresponding public key. If the signature is missing, invalid, or untrusted, the end user will receive an error or warning message.
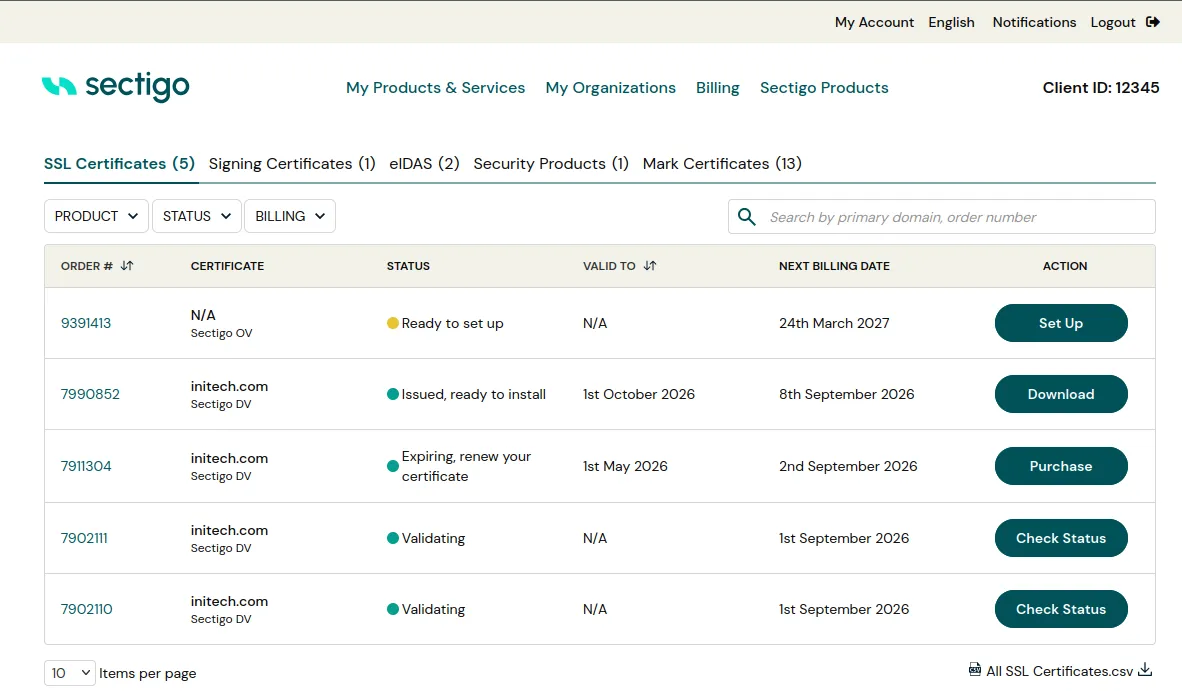
In our customer dashboard, you'll be able to view all products you have with Sectigo, view their lifecycle status, issue or reissue, and renew expiring certificates, saving you time and fear that an expired certificate may down your site at an unexpected time.
Securing some of the world’s largest and best-known brands.
Have another question?
Reach us by chat in the lower-right corner.
A code signing certificate is a digital certificate that lets software publishers sign applications, drivers and scripts. The signature shows who published the software and that it hasn't been altered since signing, so operating systems and users can trust it. Learn more in our blog: What is code signing?
Both OV and EV certificates verify your organization, protect the private key with FIPS-compliant hardware, and are valid for up to 459 days.
Yes. Sectigo can issue code signing certificates directly onto your own supported hardware security module (HSM), so no physical token is shipped. This suits CI/CD pipelines and centralized signing. We support Luna, YubiKey, Google Cloud KMS, Fortanix, YubiHSM 2 and nShield. Industry rules require the private key to be generated and stored in FIPS-compliant hardware, so software-only key storage isn't permitted. Talk to an expert to confirm your environment.
There are certain requirements that need to be fulfilled during the code signing certificate validation process. The three main things that must be verified before issuance include:
As of June 1, 2023 Code Signing certificates are:
No. Since 2024, Microsoft no longer gives EV-signed files instant SmartScreen reputation. EV and OV signed software both build reputation over time, based on your signing identity and the file itself, so a new release can still show a warning at first. A valid signature still displays your verified publisher name. To build reputation faster, sign every release with the same certificate identity, timestamp each signature, and don't modify files after signing.
A Sectigo® code signing certificate starts at $536.25 per year when customers choose the five-year option. The cost goes up for shorter time periods and for EV code signing certificates.
Since February 23, 2026, publicly trusted code signing certificates are valid for a maximum of 459 days (about 15 months), under CA/Browser Forum rules. A multi-year Sectigo plan doesn't issue one long certificate. You receive a new certificate and a new FIPS-compliant hardware token each year. Timestamp your signatures so signed software stays valid after the certificate expires.
Code Signing certificates are installed on a physical token and shipped to your location. We can only provide full refunds for products that have not been shipped. Once a product has shipped and within 30-days from order, we will refund the product cost, less shipping and token cost.
Yes. In addition to our standard token-based Code Signing Certificates, Sectigo can issue code signing certificates for use with your own supported hardware security module. This option is best suited for organizations with existing HSM infrastructure or automated signing workflows. Talk to an expert to see if this is the right fit for your environment.
We currently support Luna, YubiKey, Google Cloud KMS, Fortanix, YubiHSM 2, and nShield HSM infrastructures. Talk to an expert if you need help confirming compatibility for your environment.
Contact our team for help with your purchase or issuing your certificate.
Click the button below or click "Chat with an Expert" to start chatting with us now!
Learn about how the validity periods for digital certificates are...
A code signing certificate is a digital certificate issued by...
Code signing and the use of digital certificates underpin the...